What is Role-Based Security Awareness Training, and How Can It Be Customized and Adapted?
Role-based security awareness training matches each lesson to the risks a role actually faces. Learn how to customise and adapt it to improve compliance and strengthen defences.

On this page 13 sections
Role-based security awareness training assigns content by what a person actually does at work, so a finance approver, a developer and a field engineer are not trained on the same scenarios. It matters because generic programs are measured on attendance rather than behaviour. Gartner reports that 84% of security leaders track training completion as a top metric, while the human element appeared in 62% of breaches analysed in the 2026 Verizon Data Breach Investigations Report (p. 12).
The case for tailoring is behavioural, not statistical folklore. In Gartner research, 41% of employees admit bypassing security guidance and 61% of them know it raises risk (G00840742, February 2026, n=175). People bypass controls that do not fit the job in front of them, which is the exact problem role-based security awareness training (RBSAT is meant to solve.
This blog explores Role-Based Security Awareness Training’s benefits, customization strategies, and best practices for effective implementation, showing how tailored programs lead to stronger defenses and smarter cybersecurity practices.
What is Role Based Cyber Security Awareness Training?
Role-based security awareness training is a program that teaches each employee the risks and safe behaviors tied to their job. Finance learns invoice and payment fraud; developers, secure coding and secrets handling; HR, PII and phishing; IT, privileged access and MFA abuse; leaders, policy and risk decisions. Content is short, practical, and job-relevant, using targeted simulations, microlearning, and checklists to turn guidance into daily habits.
To put it in place, map business processes to risks, group staff by role, set clear learning paths, run realistic tests, and track role-level KPIs like click rate, report rate, and policy exceptions. Update modules as roles, tools, and threats change so training stays useful, measurable, and compliant, and reduces risk where it matters most.
Why is Role-Based Security Awareness Training Important?
Different employees encounter different cybersecurity threats. A finance team member is likely to face business email compromise (BEC) scams, while an executive is a prime target for whaling attacks. Legal professionals must protect confidential client data, and IT personnel must be aware of credential-stuffing attacks. Role-Based Security Awareness Training (RBSAT) ensures each team member receives relevant, impactful training that strengthens the organization's defense.
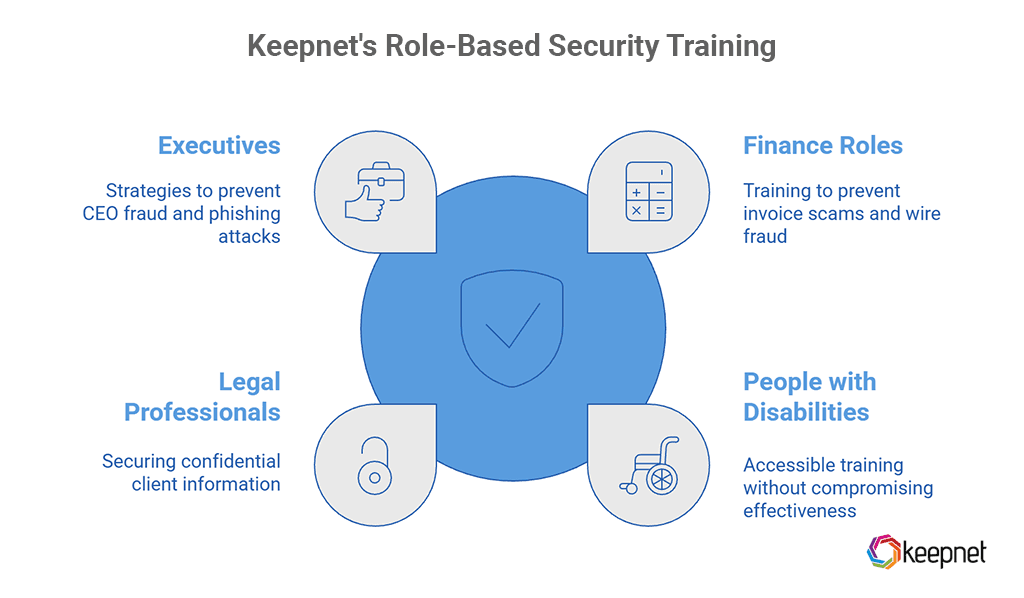
Organizations with effective security awareness training programs are 8.3 times less likely to appear on public data breach lists annually compared to general statistics. This highlights the importance of customized training, allowing different professional groups to take better precautions against specific threats.
Role-based security awareness training is essential because different job roles face unique cybersecurity risks. Tailoring training to specific roles improves both awareness and response, leading to better protection against cyber threats.
Real-world examples highlight advantage of implementing role based security awareness training various industries:
- Role-based security awareness training tailored to cultural contexts is taken more seriously than general programs.
- Using role-specific, culturally relevant scenarios increases engagement and retention.
- Cross-cultural teams developing role-based training ensure that content respects and integrates cultural nuances, boosting engagement and compliance. Netexpat report Gamified, role-based cybersecurity program increased global participation rates by 30%, by customizing challenges to regional threats relevant to specific roles. (Netexpat, 2024)
These results demonstrate that customizing cybersecurity training to each profession’s needs helps organizations reduce data breaches, safeguard sensitive information, and build a stronger security culture.
Targeted Cyber Threats: Why Role Specific Cybersecurity Awareness Matters
Different professions face unique cybersecurity threats. Below are key job roles and the cyber threats they face, emphasizing the importance of customized security training in mitigating these risks.
- Accountants and Finance Professionals face phishing attacks and fraudulent transactions. Cybercriminals use fake emails to steal credentials and initiate unauthorized transactions. Finance teams are over 30% more likely to be targeted by cyberattacks than other companies.
- Academics and researchers are prime targets for intellectual property theft and phishing scams. Cybercriminals target universities because they store large amounts of personal and research data, making them valuable targets.
- Engineers and technical staff face cyber espionage and malware threats. In 2023, a Tesla data breach caused by two former employees leaked sensitive engineering data, impacting over 75,000 individuals (The Verge). Security awareness training is essential, as 90% of data breaches are caused by human error, a risk that can be significantly reduced with proper training Isaca report.
- Legal professionals handle sensitive client data, making them prime targets for cyberattacks and social engineering scams. A Solicitors Regulation Authority (SRA) report found that 75% of law firms have been targeted, with £4 million stolen in 23 cases (Cyber Resilience Center). Strong security awareness training is crucial to safeguarding legal documents and client funds.
- Journalists and media workers are frequently targeted for surveillance and misinformation attacks. Investigations have revealed that Pegasus spyware has been used to monitor the communications of over 180 journalists across 20 countries, highlighting the pervasive threat to press freedom (CPJ).
- Healthcare workers handle sensitive medical data, making them prime targets for ransomware attacks and data breaches. Security awareness training plays a crucial role in reducing these risks by helping staff identify phishing attempts, follow data protection protocols, and respond effectively to cyber threats, ultimately strengthening the healthcare sector’s defenses.
Key Benefits of Role Based Security Awareness Training
Role-Based Security Awareness Training ensures employees receive targeted, relevant training, improving both security resilience and business continuity. Below are the key business and security benefits of implementing RBSAT in your organization.
Business Benefits
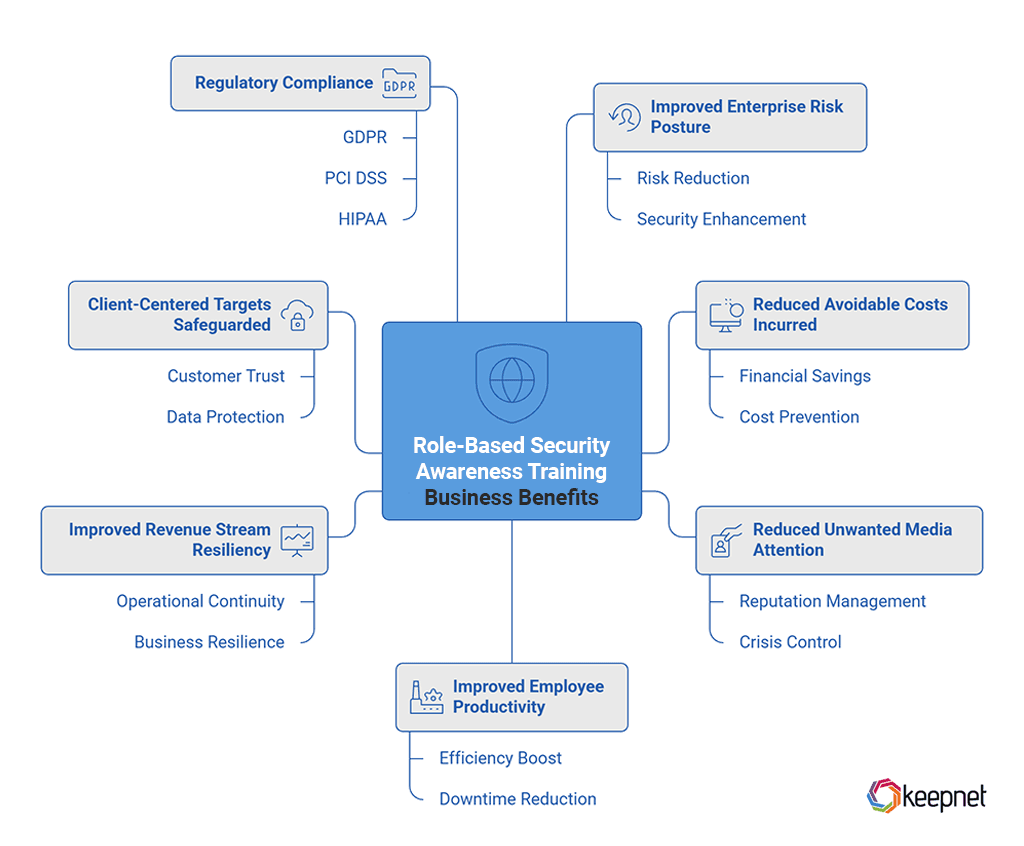
Implementing Role-Based Security Awareness Training not only strengthens cybersecurity but also helps businesses reduce costs, protect their reputation, and ensure operational continuity. Key benefits include:
- Improved Enterprise Risk Posture – Reduces human-related security risks.
- Reduced Avoidable Costs Incurred – Prevents financial losses from cyber attacks.
- Reduced Unwanted Media Attention – Helps mitigate reputation damage from security breaches.
- Improved Employee Productivity – Minimizes downtime caused by security incidents.
- Improved Revenue Stream Resiliency – Ensures critical business operations remain unaffected by cyber threats.
- Client-Centered Targets Safeguarded – Enhances customer trust by securing their data.
- Regulatory Compliance – Helps meet industry regulations like GDPR, PCI DSS, and HIPAA.
Security Benefits
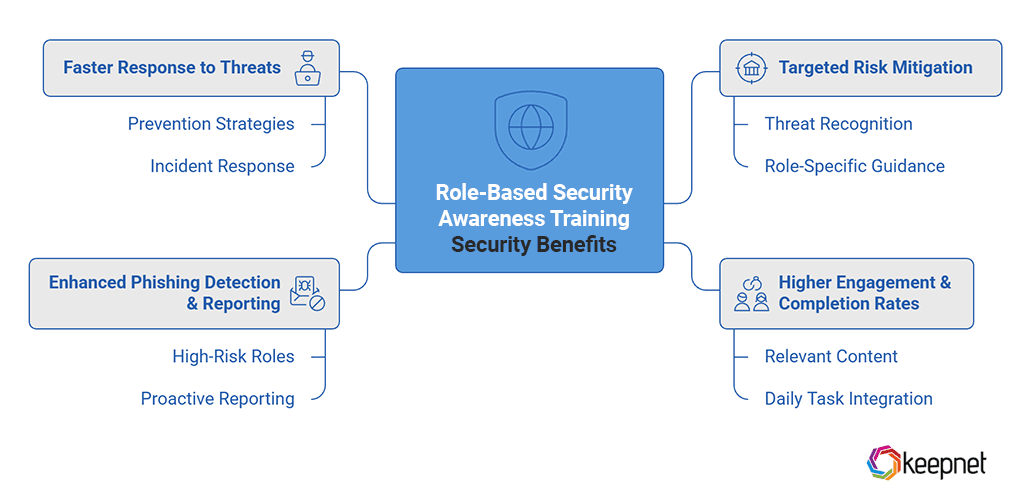
A role-based approach to security training ensures employees receive relevant guidance on the threats they face daily. This not only improves threat recognition but also enhances overall organizational resilience. Key benefits include:
- Targeted Risk Mitigation – Employees learn to recognize threats specific to their roles.
- Higher Engagement & Training Completion Rates – Employees engage more with training tailored to their daily tasks.
- Enhanced Phishing Detection & Reporting – Employees in high-risk roles become proactive in reporting suspicious activity.
- Faster Response to Threats – Employees understand their role in preventing and responding to cyber incidents.
Why Does Customization in Security Awareness Training Lead to Higher Engagement?
Security training for employees is most effective when it aligns with employees' daily tasks. When training feels relevant, employees engage more and retain information better. Job-specific scenarios make learning more impactful. For example:
- Healthcare workers respond better to scenarios about patient data breaches.
- Finance teams benefit more from phishing simulations on invoice fraud.
A National Institute of Standards and Technology (NIST) study found that segmented phishing training works because the scenario matches the job a person actually does. This proves that customized security training significantly enhances threat recognition and response.
For deeper insights, read Why CISOs Need Segmentation for a Security Behavior and Culture Program.
Content library
12,000+ lessons in 61 languages
Training for every role, language and regulation.
How Training Differs by Role: Executives, Finance and Legal Teams
Executives and leadership teams
Executives hold the most valuable access and the least time, and they deal with outside contacts all day, which makes them prime targets for CEO fraud, deepfake calls and spear phishing. Their training works best as short sessions on the attacks aimed at them, built on real, anonymised incidents, with a clear routine for verifying payment and data requests. Leadership also sets the tone: when executives take part openly and back a security behaviour and culture programme, the rest of the organisation follows.
Finance and accounts payable teams
Finance teams can move money, so attackers target them with altered invoices, fake supplier bank details, business email compromise and urgent payment requests by email, SMS or phone. Training should centre on verifying any change to bank details through a known channel, spotting BEC red flags, and a rule that no payment is approved on the strength of a single message or call, however senior the sender sounds.
Legal teams and law firms
Lawyers and legal departments handle confidential client information and constant contact with outside parties, and smaller firms often have limited security support. Attackers impersonate clients and other firms, send fake document-sharing links and try to change payment instructions. Training should cover client- and matter-specific phishing, verifying any change to payment or bank details, secure document sharing and fast reporting of anything suspicious.
Other roles follow the same pattern: IT and helpdesk staff need practice against password-reset and MFA social engineering, and HR teams against payroll and personal data requests.
What Are the Best Methods for Customizing and Adapting Security Awareness Training for Different Roles?
To build an effective, role-based security awareness training program, organizations should implement the following strategies:
- Identify Job-Specific Cyber Threats – Conduct a detailed risk assessment to determine the most relevant threats for each role, ensuring training addresses real-world risks employees face daily.
- Use Targeted Training Materials – Develop customized content, including interactive exercises, case studies, and industry-specific attack scenarios, to enhance engagement and improve retention.
- Implement Hands-On Simulations – Regularly test employees with phishing, social engineering, and ransomware simulations across multiple attack vectors like email, SMS phishing, voice call phishing , QR phishing, and MFA-phishing threats to build practical defense skills.
- Adapt Training Based on Threat Intelligence – Continuously update training modules based on emerging cyber threats, ensuring employees stay prepared for evolving attack tactics.
- Measure Effectiveness and Reinforce Learning – Track training completion rates, phishing simulation results, and employee feedback to refine the program and strengthen long-term security awareness.
To maximize the effectiveness of security awareness training, it should be combined with a phishing simulator to provide employees with realistic attack scenarios. Learn more about this approach in The Role of Adaptive Phishing Simulations in Building a Secure Culture.
Industry Insight: Ozan Ucar, Founder and CEO of Keepnet
Understanding how to enhance security awareness training is important for organizations aiming to reduce phishing risks. Ozan Ucar, Founder and CEO of Keepnet, shares valuable insights on how role-based training significantly improves engagement and phishing detection rates:
Implementing Role-Based Security Awareness Training
Successfully integrating Role based awareness training requires a structured approach to ensure employees receive targeted and effective cybersecurity education. Here are the key steps:
- Assess Role-Specific Cyber Risks – Identify unique threats based on employees' job responsibilities to ensure training aligns with real-world risks.
- Customize Training Content – Develop role-specific modules that address the security challenges employees face daily.
- Adapt Training to Behaviour: Adjust assignments as each employee’s behaviour changes; our guide to adaptive security awareness training explains how.
- Measure Training Effectiveness – Track engagement levels, phishing report rates, and incident reductions to continuously refine the program.
Keepnet assigns training automatically by role and adjusts it to each employee’s behaviour and risk level; see the security awareness training platform.
Measuring the Success of Role-Based Training
To ensure Role based security training is effective, organizations should track key outcome-driven metrics that reflect real improvements in security posture:
- Average Phishing Simulation Click Rate – Tracks how well employees identify phishing attempts. Lower click rates indicate improved awareness and reduced risk of successful attacks.
- Average Phishing Simulation Reporting Rate – Measures how often employees report phishing emails. Higher reporting rates show proactive security behavior and improved threat detection.
- Repeat Offenders Rate – Identifies employees who repeatedly fall for phishing attacks. Reducing this number indicates the effectiveness of targeted training in changing risky behavior.
- Regulatory Compliance Achievement – Ensures adherence to industry standards like GDPR, PCI DSS, HIPAA, ISO/IEC 27001, and NIST. Meeting compliance requirements demonstrates alignment with legal and organizational obligations.
For deeper insights into measuring security awareness training effectiveness, read What Are the Metrics for Evaluating Security Awareness Efforts.
Strengthening Security with Role-Based Training
Role based awareness training ensures employees receive targeted, relevant education to defend against daily cyber threats. With Keepnet Adaptive Security Awareness Training, businesses can boost engagement, strengthen defenses, and maintain compliance.
Ready to elevate your security awareness program? Contact Keepnet today and implement role-based training to protect your organization from evolving cyber threats.
Check out Keepnet's platform for human risk management and secure behaviour management to build a security-aware workforce.
"We have seen over our customer base that when security awareness training adapts to the role, engagement rate increases up to 60% with 95% completion rate, and phishing reporting increases up to 92% in less than a year."
What Better Program Design Looks Like
Role-Based Security Awareness Training, and How Can It Be Customized and Adapted? works best when the content reflects how people actually make decisions. Strong programs do not try to teach everything at once. They focus on the few behaviors that create the most risk, then reinforce them with current examples, timely reminders, and clear reporting paths.
That is also what makes training easier to defend internally. When a program changes behavior, reduces repeat-risk patterns, or improves reporting quality, leaders can see how awareness supports real business outcomes instead of acting like a standalone compliance activity.
Keepnet teams usually see the biggest gains when training is tied to a reporting path and a follow-up workflow. For most organizations, the common mistake is treating role-based security awareness training, and how can it be customized and adapted? as content delivery instead of behavior design.
Program Checklist
- Choose the user decisions that matter most instead of covering every possible topic.
- Use short modules, current examples, and realistic follow-up after incidents or simulations.
- Measure reporting, repeat risk, and remediation behavior, not only completions.
- Give managers and team leads a role in reinforcing the habits you want to build.
Frequently asked questions
Traditional security training provides generic information that applies to everyone. Role-based training, on the other hand, tailors content to the specific risks employees face in their daily work. For example, finance teams learn how to spot invoice scams, while developers focus on secure coding practices. This targeted approach delivers stronger results and higher engagement.
Industries such as finance, healthcare, legal, education, and manufacturing see the greatest impact. These sectors handle sensitive data and face unique cyber threats that generic programs cannot adequately address.
Cyber threats evolve rapidly, so organizations should review and update training content at least every six months. Incorporating current threat intelligence and recent phishing trends keeps learning materials relevant and effective.
Absolutely. AI-driven platforms like Keepnet analyze user behavior, risk levels, and learning patterns to adapt content automatically. This ensures each employee receives personalized, data-driven cybersecurity education.
Tailored security awareness programs help employees understand their specific compliance obligations. For instance, healthcare workers learn how to handle patient data securely under HIPAA, while finance teams focus on GDPR and PCI DSS requirements.
Key performance indicators include phishing simulation click rates, reporting rates, completion rates, and reduced incident frequency. Tracking these metrics helps organizations evaluate real behavioral change and return on investment.
Gamification boosts participation by turning training into an engaging experience. Using badges, leaderboards, and realistic simulations motivates employees to learn and retain knowledge longer, resulting in stronger security culture.
Organizations can use cloud-based adaptive training platforms that deliver role-specific modules online. Interactive simulations and microlearning sessions help remote employees stay engaged regardless of location or device.
Common challenges include identifying unique role risks, maintaining updated content, and aligning training with corporate culture. Partnering with experienced providers like Keepnet simplifies customization and ensures continuous improvement.
When executives actively participate and promote cybersecurity initiatives, employee engagement increases significantly. Training that is introduced or endorsed by leadership is completed more willingly and taken more seriously.
Schedule your 30-minute demo now
You'll learn how to:
- Implement Role-Based Security Awareness Training to address job-specific cyber threats effectively.
- Customize security training to boost engagement and align with industry regulations.
- Measure training success using key metrics to reduce risks and strengthen cybersecurity defenses.
30 minutes with a Keepnet specialist, on your own use cases.
Author
Ozan Ucar
Founder and CEO, Keepnet
Ozan founded Keepnet in 2017 and has worked in cyber security since 2006. He leads Keepnet's product direction and works with security teams on measuring and changing the behaviours behind incidents.